A consulting firm has quoted a readiness assessment, and the number needs approval before any remediation begins. Or an enterprise customer has made a SOC 2 report or an ISO 27001 certificate a condition of signing, and procurement has already suggested a name it knows.
Either way, finance is asking what the compliance line actually buys, and the answer so far is a rate card and a scope.
That is where most searches for the best Deloitte competitors start. Deloitte is a legitimate choice: a licensed CPA firm with an attestation practice, a name procurement recognizes, and a readiness offering described on its own third-party assurance page.
This guide is for the buyer who wants to know what else is on the table, and it compares every option on the same four questions. What does the firm do. What stays on your team. Who signs the report. What does it cost, and is the fee ever at risk.
The firms here deliver readiness in one of two ways, and one provider delivers it a third way.
Advisory and attestation firms assess your controls, recommend fixes, and, if they are licensed CPA firms, examine the result and sign the report; the remediation between those two engagements is yours.
Accredited certification bodies do the same for ISO 27001 and are barred by their accreditation from building the ISMS they certify.
A service performs the work: policies written, controls mapped, evidence collected, auditor coordinated, with the customer's team reviewing and signing.
This guide compares 9 companies like Deloitte and the one provider that does not work like Deloitte: three Big Four assurance practices, one mid-tier CPA firm, three specialist assessment firms, one global certification body, and EasyAudit. Every firm is described from its own published material; where a fact could not be sourced, it appears as a question for you to ask that firm.
We built EasyAudit, so read our take on our own service with that in mind. The scoring is published below, and we scored ourselves on the same seven criteria as everyone else.
The verdict in a nutshell: EasyAudit is the best overall pick for regulated companies that need a committed SOC 2 or ISO 27001 readiness date and want the work performed rather than advised on. The Compliance Simulation is free, takes about 75 minutes of scheduled time across two calls, and the report is yours either way.
Among the firms, A-LIGN is the strongest single-provider audit practice, Schellman is the pick when SOC 2 and ISO 27001 run concurrently, and PwC leads the Big Four on SOC 2+ combined reporting. BSI is the certification body to name when the ISO certificate's issuer matters to your customers.
Best Overall | Best Single-Provider Audit Practice | Best for Concurrent SOC 2 and ISO 27001 | Best Big Four Option for SOC 2+ Reports |
EasyAudit | A-LIGN | Schellman | PwC |
Deloitte Competitors for SOC 2 and ISO 27001 Readiness: Comparison Chart
Provider | Best For | Delivery Model | What They Do For You | What Stays On Your Team | Who Signs the Report | vs. Deloitte | Score |
EasyAudit | Best Overall | Service | Runs the program: policies written, controls mapped, evidence collected, fixes prescribed, auditor coordinated. A named human expert leads. | Business knowledge, review, sign-off. Under ten hours a year in steady state. | An independent CPA auditor or accredited certification body. EasyAudit never signs. | Performs the work Deloitte advises on; diagnoses free before commitment; fee at risk on the date. | 9.3 |
A-LIGN | Best Single-Provider Audit Practice | Advisory and attestation | Readiness assessment and the audit or certification from one licensed and accredited firm, with the A-SCEND platform for evidence. | Remediation and program operation. A-LIGN identifies gaps; your team closes them. | A-LIGN, as a licensed CPA firm and accredited ISO certification body. | Same advisory-and-attest model at specialist scale, with a free-tier evidence platform. | 7.7 |
Coalfire | Best for Cloud Service Providers and Multi-Stand ard ISO | Advisory and attestation | Readiness assessment, mock audit, attestation through Coalfire Controls and ISO certification through Coalfire Certification. Compliance Essentials platform. | Remediation and program operation between assessments. | Coalfire Controls (CPA) for SOC; Coalfire Certification (ANAB, UKAS) for ISO. | Same model, deeper with cloud service providers, several ISO standards under one accredited body. | 7.5 |
Schellman | Best for Concurrent SOC 2 and ISO 27001 | Advisory and attestation | Attestation and ISO certification by Schellman & Company; non-attest readiness by Schellman Compliance. | All remediation and program operation. Readiness advice is guidance, not execution. | Schellman & Company, licensed CPA firm and ANAB and UKAS accredited body. | Same model with independence built into the structure; concurrent SOC 2 and ISO 27001. | 7.4 |
BSI | Best for ISO 27001 Certification From a Global Body | Advisory and certification | ISO 27001 certification through BSI Assurance; ISMS implementation, internal audits and SOC 2 readiness through a separate consulting practice. | Remediation and ISMS operation unless BSI Consulting is engaged; the certifying arm cannot advise on what it certifies. | BSI Assurance for ISO certificates. BSI does not issue SOC 2 reports. | Different model: a certification body first, with consulting kept separate for impartiality. | 6.8 |
PwC | Best Big Four Option for SOC 2+ Combined Reports | Advisory and attestation | SOC readiness assessment (gap identification, recommendations), SOC examination, SOC 2+ combined reports. | All remediation and program operation between readiness and examination. | PwC, as a licensed CPA firm. | Closest peer: same Big Four model; publishes SOC 2+ combined reporting explicitly. | 6.6 |
BDO | Best Mid-Tier CPA Firm for SOC Reporting | Advisory and attestation | Readiness assessment to identify and rectify compliance gaps, then the SOC 1, 2, 2+ or 3 report; free initial consultation per its own page. | Remediation and program operation between readiness and examination. | BDO, as a licensed CPA firm. | Same model from a mid-tier national firm; free consultation and estimate offered up front. | 6.6 |
KPMG | Best for Regulated Financial Services | Advisory and attestation | SOC readiness review (workshops, interviews, documentation review, roadmap) and SOC attestation; ISO 27001 implementation support via member firms. | All remediation and program operation between readiness and examination. | KPMG, as a licensed CPA firm, for SOC. ISO certificates come from a separate accredited body. | Same Big Four model; readiness review published in unusual detail. | 6.3 |
EY | Best for SOC Attestation With a Dedicated ISO Certification Body | Advisory and attestation | SOC readiness assessment (control review, gap analysis, documentation evaluation, recommendations), SOC examination, ISO certification through EY CertifyPoint. | All remediation and program operation between readiness and examination. | EY for SOC reports; EY CertifyPoint, a dedicated accredited body, for ISO certificates. | Same Big Four model, with a dedicated global ISO certification body, EY CertifyPoint. | 6.2 |
Delivery model: Service means the provider's people perform the recurring compliance work. Advisory and attestation means the firm assesses readiness and, as a licensed CPA firm, examines and signs the SOC report; remediation in between is the customer's. Advisory and certification means the same structure for ISO 27001 through an accredited certification body.
Data current as of September 2026. No firm in this comparison publishes a rate for readiness or attestation work. Every firm description is drawn from that firm's own published service pages; where a fact could not be sourced there, the entry poses it as a question for the buyer to ask.
Why Look for Alternatives to Deloitte?
Three reasons come up, and every one of them starts from what Deloitte says about its own offering rather than from anything said about it. Deloitte's third-party assurance page describes the practice as advising on control effectiveness and performing attestation engagements, with SOC 1 and SOC 2 reporting alongside FedRAMP and HITRUST.
Read plainly, that is a diagnosis and an opinion. Here is what follows from it.
The engagement is advisory and attestation, and the work returns to your team
A readiness assessment identifies gaps and recommends improvements. An attestation engagement examines the controls and signs the report. Neither is the work of writing the policies, closing the findings, collecting the evidence and keeping the program current, and Deloitte's own page does not describe that work as part of the offering.
If your reason for buying is that nobody internal wants to run the program, ask any firm this question before you scope: after the readiness report lands, who performs the remediation, and who is accountable for the program between the examination and the next one?
Readiness and attestation are two engagements, and independence has to be documented
Under the AICPA Code's independence and nonattest-services rules, a firm that designs and implements controls generally cannot attest to those same controls where doing so impairs its independence, because an auditor must not audit its own work. The rules are not a blanket ban; independence is evaluated for the actual combination of services.
In practice that often means one firm for readiness and another for the examination, or a carefully bounded readiness scope from the firm that will sign. Ask Deloitte, and every firm on this page that offers both, to document its independence conclusion in writing for your engagement before you sign. A firm that never signs the opinion has removed the question.
The practice is structured for enterprise engagements
This is a fit problem, not a quality problem. Deloitte's assurance practice is built around large clients and integrated with financial audit relationships, and its published SOC material sits inside a broader compliance and regulatory offering.
A 200-person insurer or a regional data center operator buys the same staffing model and the same engagement cadence that a Fortune 500 client does.
For that buyer the questions are practical: how is the team staffed at my scale, what does the engagement cost relative to my compliance budget, and is a Big Four letterhead what my customers require, or what procurement is used to seeing?
None of those is a reason not to choose Deloitte. Brand comfort in procurement is real, and a buyer whose enterprise customers scrutinize the letterhead, or whose financial auditor is already Deloitte, has a sound reason to consolidate. The rest of this guide is for the buyer who wants to compare on the date, the economics and who performs the work.
How We Evaluated These Deloitte Alternatives
Every provider here was scored one to ten on seven criteria, then weighted. The weights are published so you can add up the numbers yourself. They come from what buyers ask about before they buy, not from where any one provider is strongest: how the work gets done, what it costs and on what terms, how long it takes, and how the audit is handled.
Our Scoring Methodology
Criterion | Weight | What we looked for |
Work performed for you versus work left on your team | 25% | Who writes the policies, maps the controls, chases the evidence and talks to the auditor. The single biggest question on 60 percent of sales calls. |
Pricing clarity and commitment terms | 20% | Whether a buyer can see a program price before signing, what the second framework costs, and what happens at renewal. Pricing questions appear on 51 percent of calls. |
Timeline certainty and consequence if missed | 15% | Whether the provider commits to a date, and what it costs the provider if the date slips. |
Assurance handling and independence | 15% | Who issues the result, whether that party is a licensed CPA firm or an accredited certification body where the framework requires one, whether the provider that prepared you can also sign, and how independence is documented. |
Multi-framework reuse | 10% | Whether the second and third frameworks reuse the controls and evidence from the first, or start a new project. |
Environment fit | 10% | Microsoft-heavy estates, on-prem systems, data center and contact center floors, and other operations that cloud-native tooling was not built for. |
Evidence a third party will accept | 5% | Approvals recorded with who and when, an audit trail the application cannot bypass, and read-only access for the auditor, certification body or reviewer. |
We weight the first criterion heaviest because it is where readiness engagements fail after signature. A firm that writes the readiness report hands the remediation back, by design and often by rule. The buyer discovers where the work sits about six weeks in, when the gap list has owners on their side and nobody on the firm's, and by then the date has already moved.
Provider | Work (25%) | Pricing (20%) | Timeline (15%) | Assurance (15%) | Multi-framework (10%) | Environment (10%) | Evidence (5%) | Weighted |
EasyAudit | 10 | 8 | 10 | 9 | 10 | 9 | 9 | 9.3 |
A-LIGN | 7 | 7 | 7 | 9 | 8 | 9 | 9 | 7.7 |
Coalfire | 7 | 6 | 7 | 9 | 8 | 9 | 9 | 7.5 |
Schellman | 6 | 5 | 7 | 10 | 9 | 9 | 10 | 7.4 |
BSI | 6 | 5 | 6 | 8 | 8 | 9 | 10 | 6.8 |
PwC | 5 | 4 | 6 | 9 | 9 | 9 | 10 | 6.6 |
BDO | 5 | 5 | 6 | 9 | 8 | 8 | 9 | 6.6 |
KPMG | 5 | 4 | 5 | 9 | 8 | 8 | 10 | 6.3 |
EY | 5 | 4 | 5 | 9 | 7 | 8 | 10 | 6.2 |
Weighted totals are rounded to one decimal. The score on each provider entry, the score in the comparison chart, and this table reconcile. Ties are broken on the first criterion, then the second. Every provider carries identical scores on every page of this series; the one exception is EasyAudit's timeline score on the NIST CSF page, explained there, because no fee is at risk on CSF itself.
9 Best Deloitte Alternatives in 2026 Reviewed
Who are Deloitte's competitors for SOC 2 and ISO 27001 readiness? The other Big Four assurance practices, the mid-tier CPA firms, the specialist assessment firms and certification bodies, and one provider that performs the work instead of advising on it.
Here is how they compare on the test that matters after signature: who does the work, who signs the report, and what happens if the date slips.
1. EasyAudit
Best for: regulated companies that need a committed SOC 2 or ISO 27001 readiness date and want the work performed rather than advised on.
Compliance Service Score: 9.3/10
Service Overview
EasyAudit is a compliance service for organizations that have to be compliant and do not want to do it themselves. A named human compliance expert leads your engagement from start to finish, the AI Compliance Officer executes the recurring work, and the platform is the shared foundation and memory. One service, not three products.
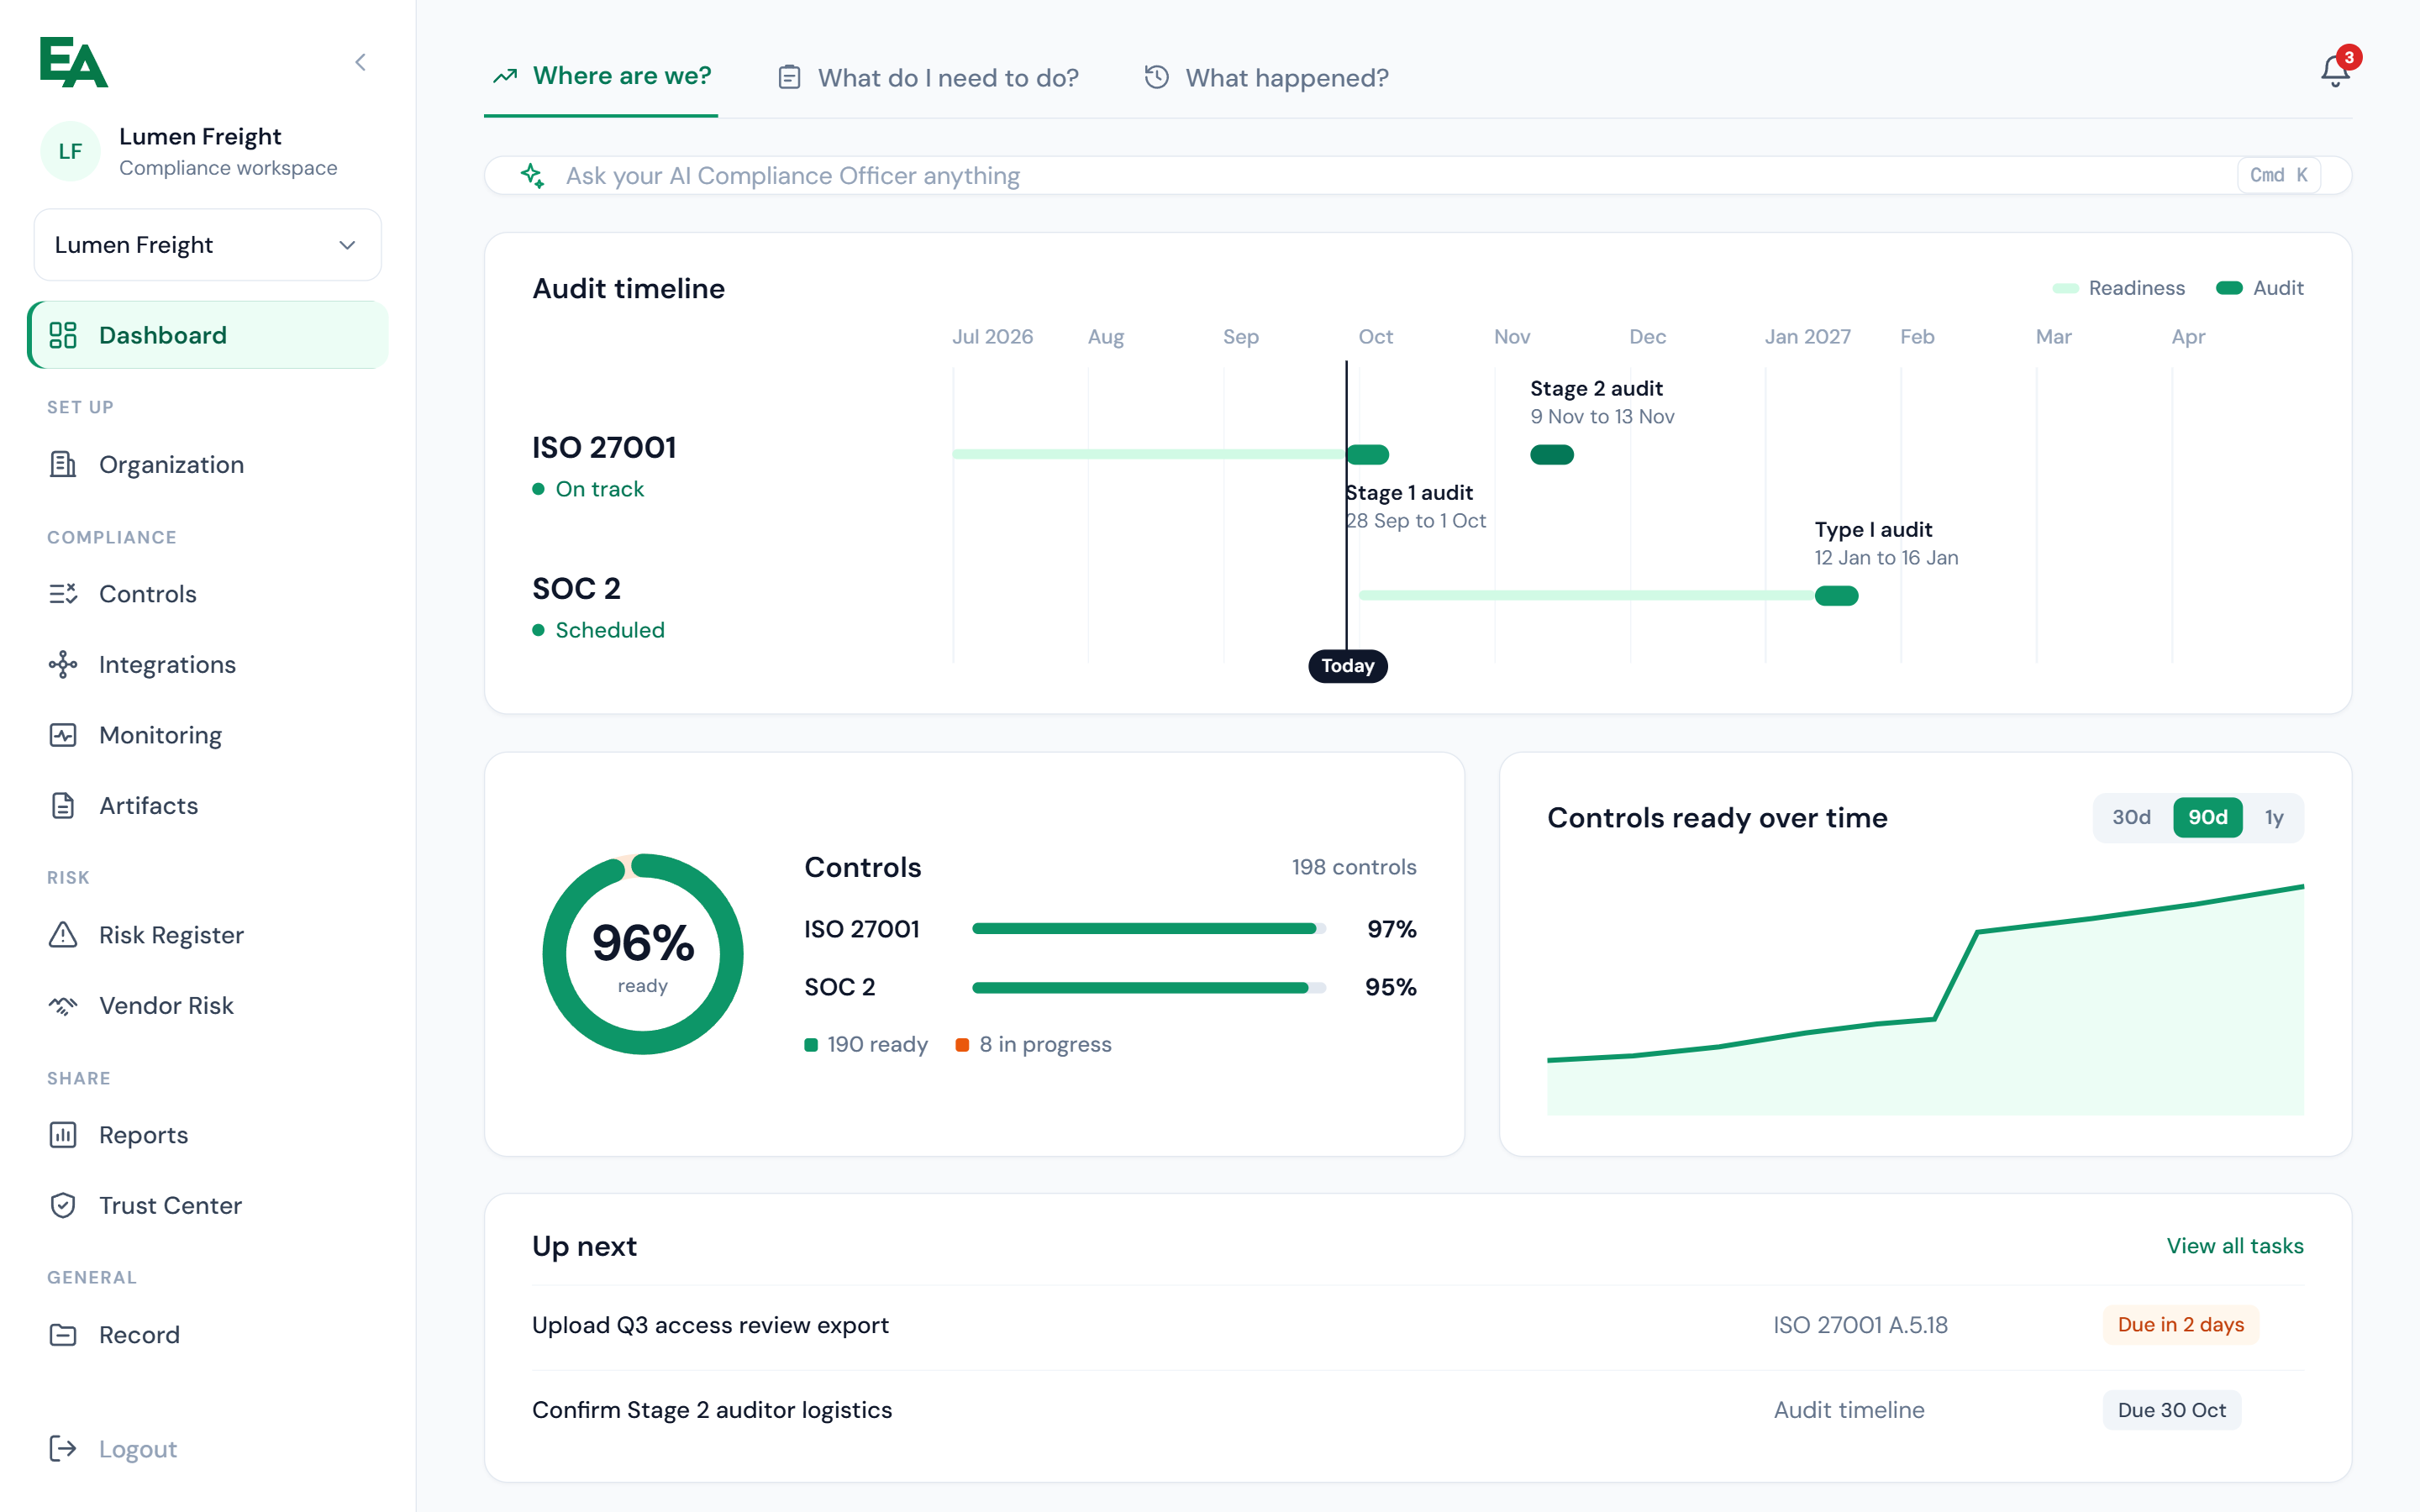
Our founder came out of Deloitte's risk advisory practice, which is why we know exactly how a readiness assessment is scoped and priced, and why we give ours away.
If a deal, a renewal, a contract or a regulator is waiting on your report or certificate, and the quote in front of you is for an assessment that leaves the remediation with your team, we built it for you, and we built it for regulated companies: the ones whose customers, regulators, insurers or contracts require proof, in whatever industry that pressure arrives.
Two things set us apart in this guide:
We diagnose before you commit, at no charge: the free Compliance Simulation runs on your real environment and returns your readiness, gaps, timeline and price before you sign anything.
Then we lock the date at signature and put our fee behind it.
The 3 Readiness Problems We Built EasyAudit to Solve
The readiness assessment is paid, and it is a diagnosis
Every firm in this guide sells a readiness assessment before any remediation begins, scoped and priced as its own engagement. It tells you how far from ready you are. It is a paid diagnosis, and the buyer pays for it before knowing what the program will cost.
We run the Compliance Simulation on your real environment for free, in about 75 minutes of scheduled time across two calls. You leave with your readiness per framework, every material gap prioritized, the work required, a dated timeline, the investment, and a written recommendation from the expert who ran it. The report is yours either way. Diagnose first, commit second.
The engagement ends and the work comes back
Advisory engagements deliver a gap list, recommendations and a roadmap, and the recurring work returns to your team when the engagement closes. Between examinations the engagement is complete, and the report describes the week of the audit rather than the year that follows.
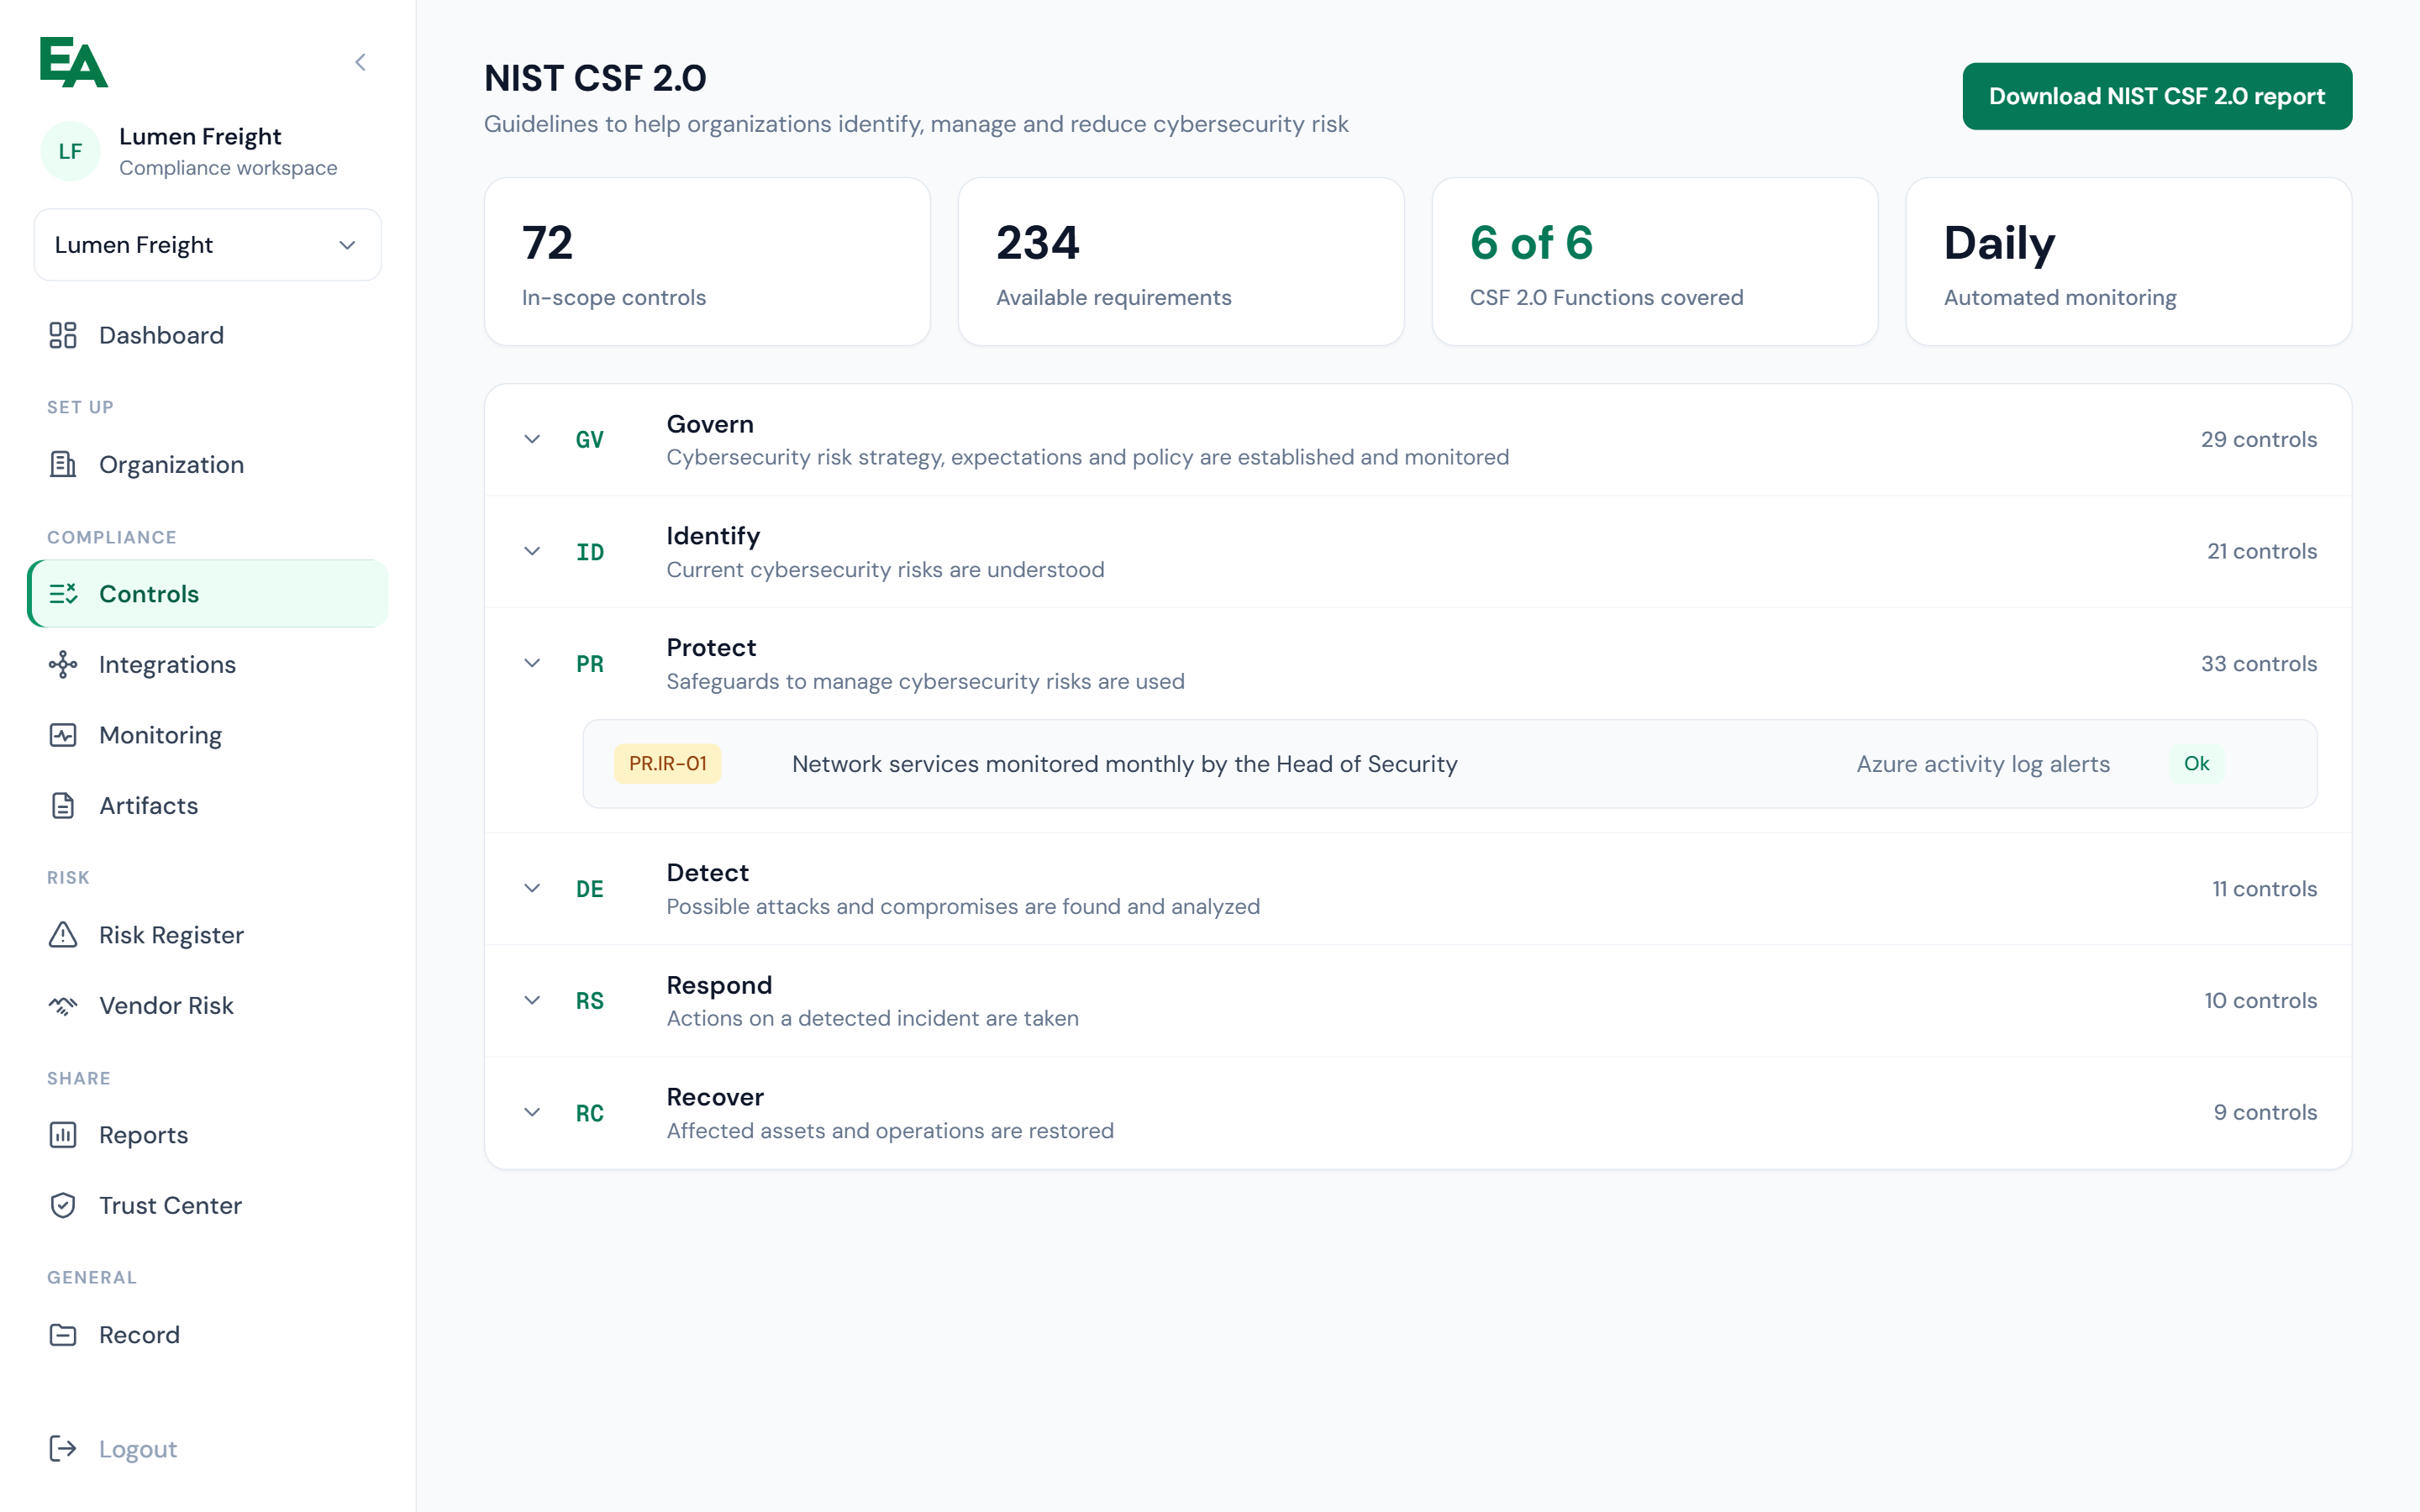
We transfer the work and keep it. Our AI Compliance Officer drafts the policies, collects the evidence and prescribes the exact fix. Our named compliance expert reviews every piece of work and coordinates your auditor directly. After the first audit, 3,950+ continuous monitoring checks keep the program true between examinations. The work does not disappear. It changes owners, and it stays changed.
No firm commits to a date
Firms bill by scope whether you pass or not. Certification bodies audit when you say you are ready. The compliance industry guarantees nothing, and the deal in procurement keeps waiting.
We lock a date at signature and put our fee behind it. Audit-ready and submitted to an independent auditor or accredited certification body by the committed date, or you do not pay. The Audit-Ready Guarantee applies to eligible engagements and covers readiness and submission.
The auditor or certification body alone determines the result, and that boundary sits next to the guarantee every time we state it.
Frameworks Covered
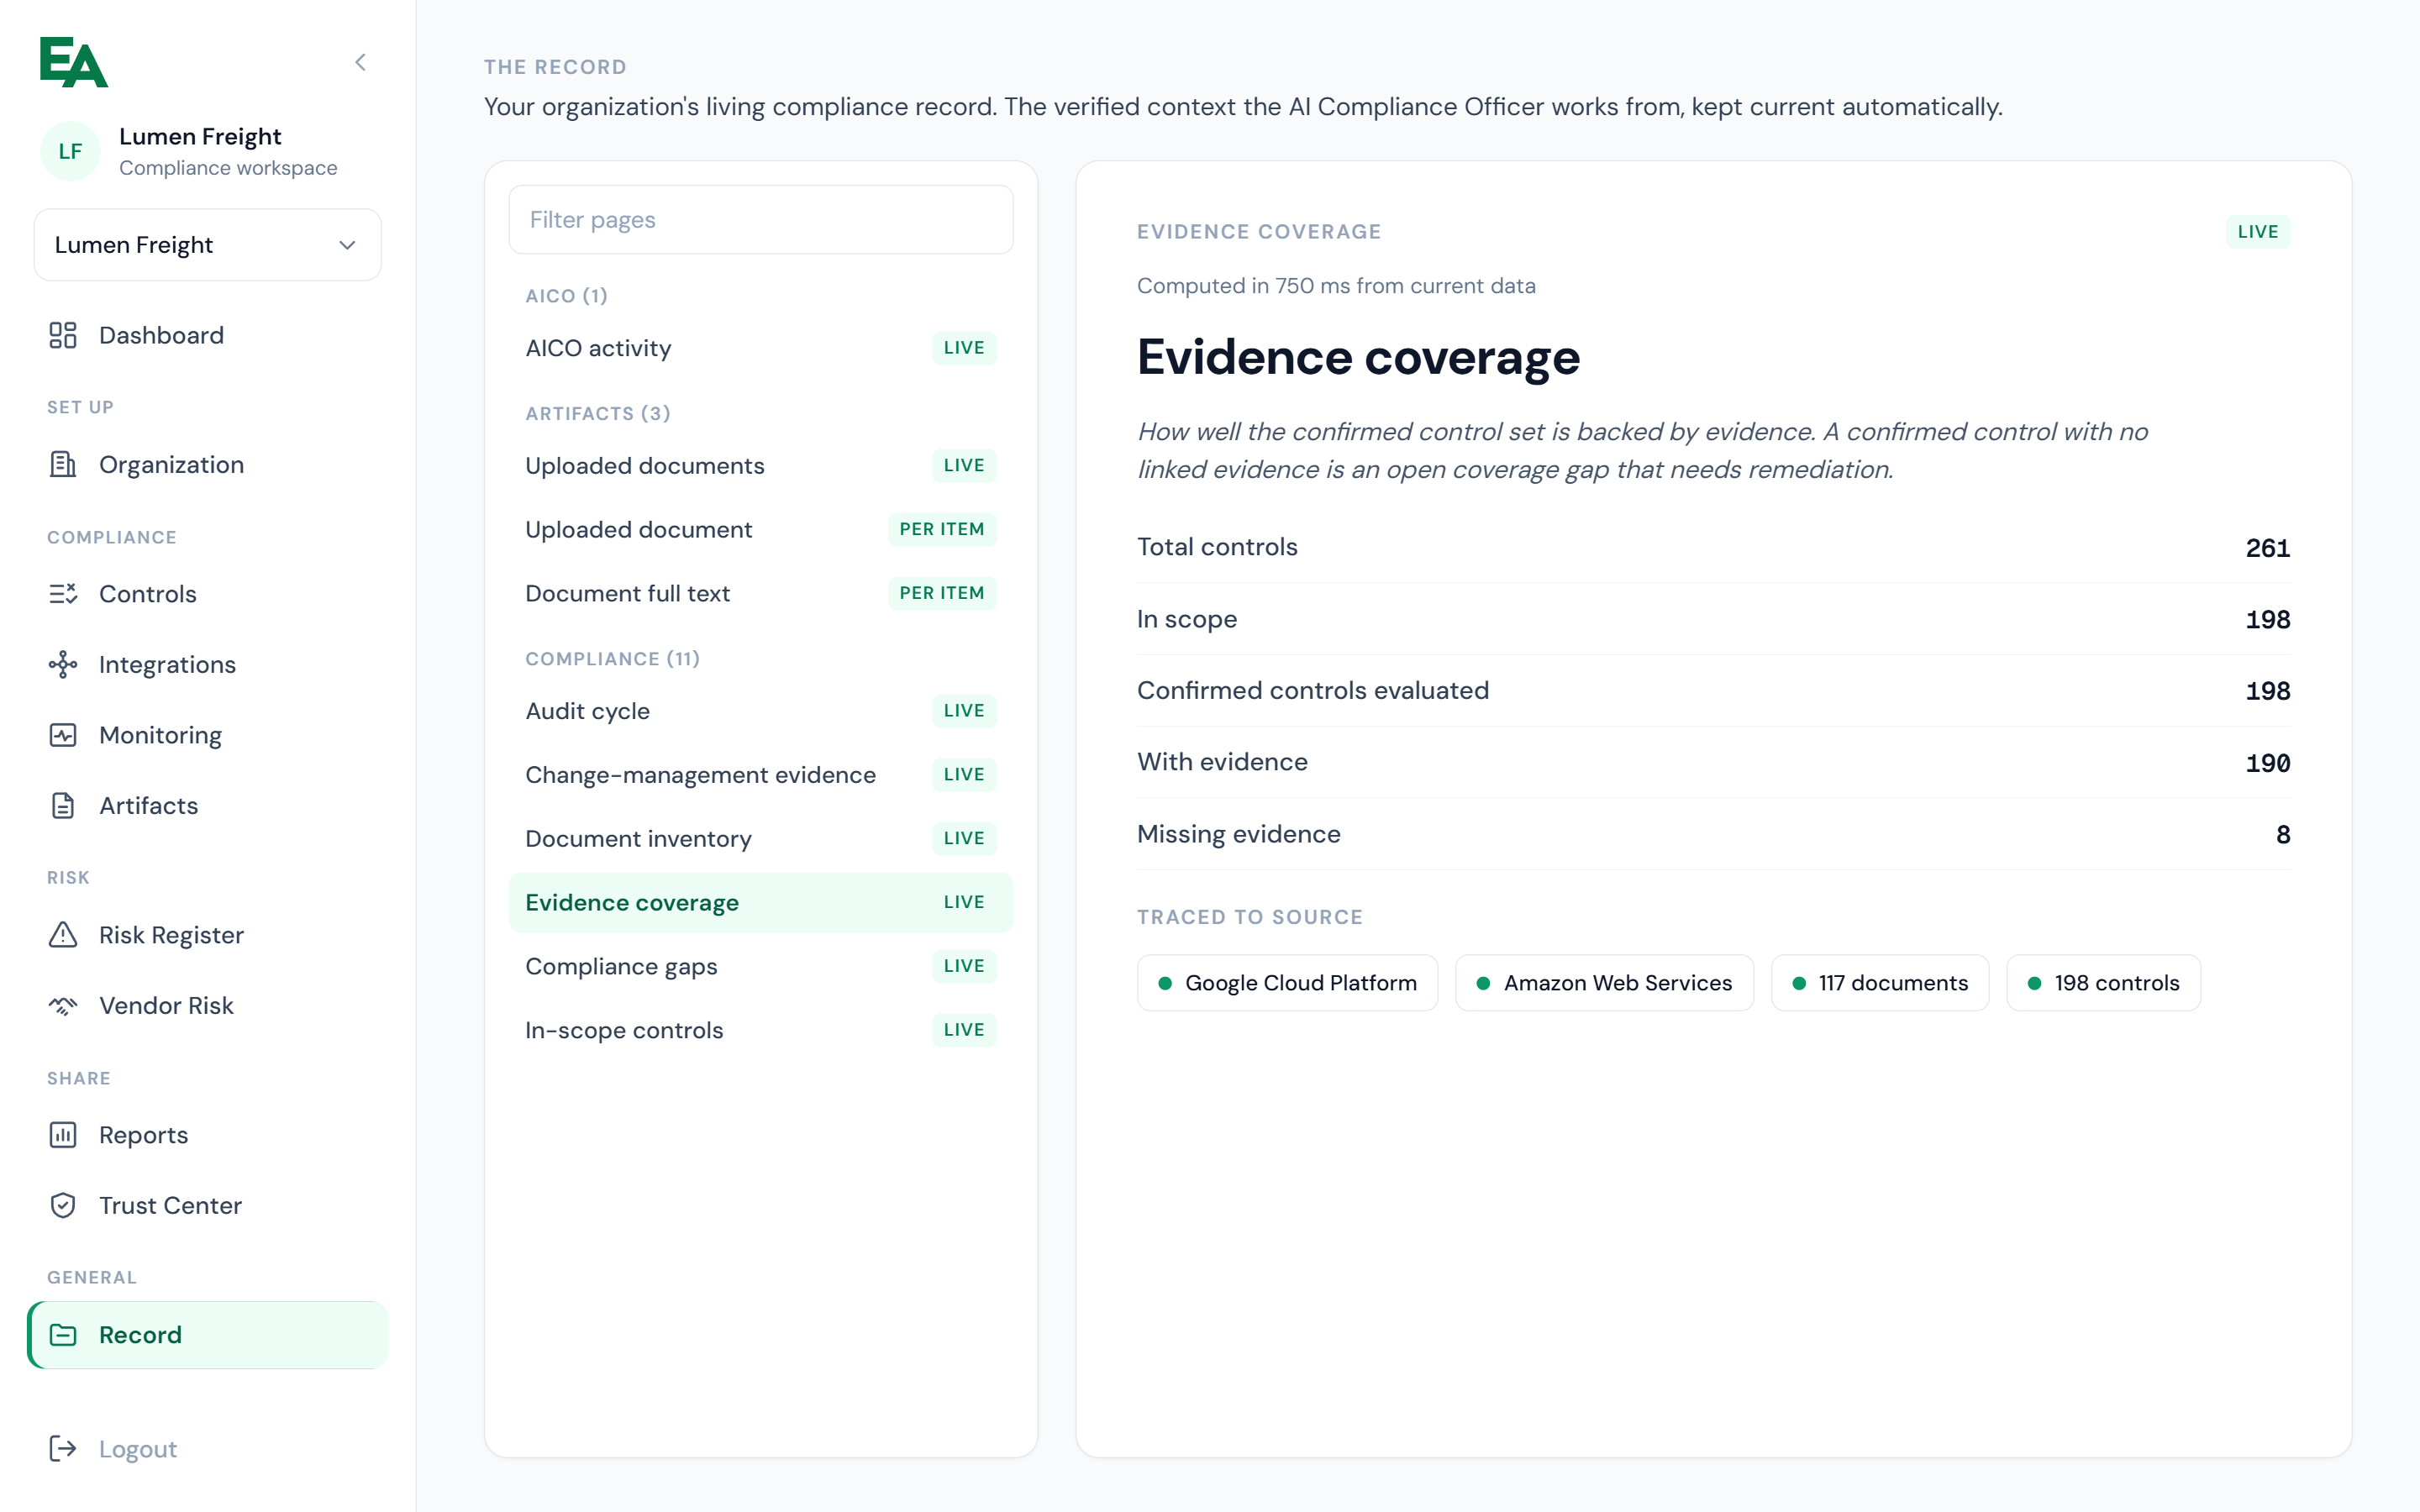
SOC 1, SOC 2, ISO 27001, ISO 42001, ISO 9001, NIST CSF 2.0 and CMMC. One control library sits under all seven, so one control can satisfy up to seven frameworks and the program carries 60 to 70 percent fewer controls than running frameworks in parallel. Your first framework becomes the foundation for every framework that follows. The second framework is not a second project.
Pricing and Engagement Model
The investment is fixed at signature, from the Compliance Simulation run on your own environment, and the Simulation Report is the proposal. There is no paid readiness assessment, no hourly rate card and no scope that expands after the gap list lands. For a directional figure before the Simulation, use the cost calculator.
The comparison that holds is against service spend: the readiness assessment fee, the advisory hours during remediation, and the internal time your team spends between engagements. We replace all three. Auditor and certification body fees remain separate, because the independent auditor issues the result. We are not the lowest-priced option in this guide, and we say so under Tradeoffs.
The Audit-Ready Guarantee
Audit-ready and submitted to an independent auditor or accredited certification body by the date committed at signature, or you do not pay. The guarantee applies to eligible engagements and covers readiness and submission. It does not cover the auditor's opinion or the certification body's decision, and no provider can cover those.
The reason we can make it is the order of operations: the Simulation scores your readiness on your real environment before we commit, so the date is calculated, not hoped for.
What Stays On Your Team
Under ten hours a year from your team in steady state, because the recurring work transfers to us rather than shrinking on your calendar. Your team supplies business knowledge, reviews key decisions, and signs where its authority is required. We write the policies; your team reviews and signs. Controls are accepted in one click with who-approved-and-when recorded.
One 15-minute meeting closes three to four evidence items. Signed-statement templates mean you never hit a dead end.
Setup
The Compliance Simulation runs on your real environment in about 75 minutes of scheduled time across two 30-minute calls. A mutual NDA is signed the same day, documents go into a workspace without cleanup, a scoping questionnaire is completed, and read-only connections go live on the first call.
The environment is pre-built before you join the second call, where decision makers see readiness per framework, gaps, scope, price and the committed date on their own data. Access is read-only by design, using temporary credentials and OAuth.
Tradeoffs
Brand comfort with a large consulting firm is real in procurement-heavy organizations, and it is a legitimate reason to choose one; we compete on the date and the economics, not on brand. Licensed CPA firms in this comparison can issue the SOC 2 opinion, and accredited bodies can issue the ISO certificate; we never issue either and never will.
Large consulting firms sell services well outside compliance readiness, and a buyer who needs strategy, technology implementation or tax alongside readiness has a reason to consolidate. We are not built for a 1 to 10 person company or a cloud-native SaaS chasing a single framework with no external pressure.
A large GRC team that wants to run the program itself with outside advice will prefer an advisory engagement. We cost more than a software seat, and the guarantee covers readiness and submission by the committed date for eligible engagements, not the result.
Support
Your named compliance expert owns the engagement end to end. They set the plan, check every piece of work, deal with your auditor or certification body directly, and you hear from them every two days. If the controls require it, they attend your facility: data center floors, contact center floors and FDA-regulated manufacturing are inside scope. You never have to log in; you always can.
Mini Case Study
OutreachGenius runs AI-driven lead follow-up for home service franchise networks, a business built on outbound calls, SMS and call recording, where TCPA consent and brand-safe outreach are conditions of operating.
Enterprise franchise buyers blocked deals until the company could show a SOC 2 report, and with a team of six there was nobody to run a readiness program or manage a consulting engagement. We ran the program, from controls and policies to evidence and CPA coordination, and the blocked deals moved.
2. A-LIGN
Best for: buyers who want the readiness assessment, the evidence platform and the signed report or certificate from one licensed and accredited firm.
Compliance Service Score: 7.7/10
A-LIGN calls itself the top SOC 2 issuer in the world, with more than 3,500 SOC 2 assessments completed, over 100 SOC 2 auditors, and accreditation as an ISO 27001, ISO 27701 and ISO 22301 certification body. It is the most complete single-provider answer among Deloitte alternatives for a buyer who wants readiness, evidence tooling and the signed report from one firm.
Service Overview
A-LIGN recommends a readiness assessment for first-time candidates, identifying high-risk control gaps and giving the organization time to remediate before the examination. Its A-SCEND platform centralizes evidence collection and audit requests and lets submissions be reused across frameworks. A-LIGN then performs the SOC 2 examination or the ISO 27001 certification audit and issues the result.
It partners with the major compliance platforms, so a customer can bring its own tooling.
Pricing and Engagement Model
Quote only, scoped to the engagement. A-LIGN publishes no rates. A-SCEND's automation and audit-readiness features are offered on a free tier per A-LIGN's own site, with the audit priced separately. Ask what the readiness assessment costs and what it produces, and how the audit is priced across a three-year ISO cycle.
What Stays On Your Team
Remediation and program operation. A-LIGN identifies the gaps and audits the result; the controls, policies and evidence in between are your team's responsibility or a separate provider's.
Who Signs the Report
A-LIGN, as a licensed CPA firm for SOC reports and an accredited certification body for ISO certificates. Because the same firm advises and attests, ask A-LIGN to document its independence conclusion for your combination of services, which accreditation and AICPA rules require it to be able to do.
Tradeoffs
A-LIGN is a strong choice when you want the readiness assessment and the audit from a single licensed firm, when FedRAMP or HITRUST runs alongside SOC 2, and when the letterhead matters less than the volume of reports issued. It is not an outsourced program: the work between readiness and audit is yours.
A Gartner Peer Insights reviewer described pricing as reasonable; another criticized billing practices on a disputed audit date.
3. Coalfire
Best for: cloud service providers and organizations certifying to several ISO standards at once, with a mock audit from certification body staff before the real one.
Compliance Service Score: 7.5/10
Coalfire is a cybersecurity services firm that delivers more than 500 SOC reports a year through Coalfire Controls, a licensed CPA affiliate, and certifies management systems through Coalfire Certification, accredited by ANAB since 2015 and UKAS since 2019. Three quarters of its SOC engagements are for cloud service providers, by its own figures.
Service Overview
Coalfire's readiness assessment identifies and documents controls, determines gaps and recommends remediation before a Type I or Type II report. For ISO 27001 a lead auditor facilitates the readiness assessment and offers a mock audit conducted by certification body staff. Compliance Essentials, its platform, coordinates evidence across 80-plus frameworks, and Coalfire offers combined reports such as SOC 2 with HIPAA or CSA STAR.
Pricing and Engagement Model
Quote only, scoped by engagement. Coalfire publishes no rates, and its AWS Marketplace listings for SOC and ISO readiness require a quote. Ask what the readiness assessment and the mock audit cost separately, and how the three-year ISO lifecycle is priced.
What Stays On Your Team
Remediation and program operation between assessments. Coalfire documents controls and runs the mock audit; the customer implements. One published customer account describes hiring a separate firm to perform the required ISO risk assessment and internal audit before Coalfire's certification audit.
Who Signs the Report
Coalfire Controls, a licensed CPA firm, for SOC reports; Coalfire Certification, an accredited body, for ISO certificates. Ask Coalfire to document the independence conclusion where the same organization advises and attests, and clarify which entity signs.
Tradeoffs
Coalfire's strength is depth with cloud service providers and breadth across ISO standards under one accredited body. For a 200-person insurer or data center operator that depth costs more than a mid-market buyer may need, and the model is advisory: the work stays with your team, and impartiality rules mean the certifying arm cannot close the gaps it finds.
4. Schellman
Best for: organizations pursuing SOC 2 and ISO 27001 concurrently that want one accredited firm for both, with independence built into the firm structure.
Compliance Service Score: 7.4/10
Schellman is one of the largest independent SOC examination providers in the United States, issuing more than 2,000 SOC reports a year, and an ANAB and UKAS accredited ISO 27001 certification body. It runs a split structure: Schellman & Company performs attest and certification work, and Schellman Compliance performs non-attest readiness and advisory, which keeps independence intact while both sit under one roof.
Service Overview
Schellman performs the SOC 2 examination and issues the report, and performs Stage 1 and Stage 2 for ISO 27001 and issues the certificate. Its readiness assessment, offered through the non-attest entity, identifies gaps and recommends remediation before the formal engagement.
A single-assessor approach lets an organization pursue SOC 2 and ISO 27001 concurrently under one firm, and Schellman was the first ANAB-accredited certification body for ISO 42001.
Pricing and Engagement Model
Quote only, scoped to the engagement, the criteria selected, the report type and the size of the environment. Schellman publishes no rates. Ask for the full cycle priced up front: readiness, examination, and for ISO the two surveillance audits and recertification.
What Stays On Your Team
All of it. Schellman assesses readiness and attests; it does not implement the controls, write the policies or collect the evidence. Your team, or a separate provider, performs the remediation between the readiness assessment and the examination.
Who Signs the Report
Schellman & Company, as a licensed CPA firm and accredited certification body. The split between Schellman & Company and Schellman Compliance is how the firm documents independence; ask for that documentation for your engagement.
Tradeoffs
Schellman is the firm to shortlist when your customers scrutinize the auditor and you need SOC 2 and ISO 27001 examined together. It is not a readiness service in the working sense: the assessment tells you what is wrong, and the fixing is yours. There is no committed readiness date, because Schellman's commitment is to the examination, not to your remediation.
5. BSI
Best for: organizations that need the ISO 27001 certificate from the body enterprise procurement teams recognize first, with implementation help from a separate consulting practice.
Compliance Service Score: 6.8/10
BSI is the certification body most enterprise procurement teams recognize by name, and the body on the certificate for many organizations in this category, including Deloitte's own ISMS in several regions per Deloitte's announcements. BSI Assurance issues ISO 27001 certificates; a separate BSI consulting practice offers ISMS implementation, internal audits for certification readiness, and SOC 2 readiness and implementation.
Service Overview
BSI Assurance performs Stage 1, Stage 2 and the surveillance and recertification audits across ISO 27001, ISO 27701, ISO 22301, ISO 9001 and ISO 42001.
BSI's consulting arm, per its own service pages, offers ISMS development and enhancement, risk assessment, governance and policy creation, internal audits for certification readiness, and SOC 2 readiness aligned to the AICPA Trust Services Criteria with pre-assessment and audit readiness support.
Pricing and Engagement Model
Quote only, scoped by engagement. BSI publishes no rates for certification or consulting. Ask for the full three-year ISO cycle priced up front, and ask separately for the consulting scope if you want implementation help.
What Stays On Your Team
If you engage BSI Assurance alone: everything except the audit. If you also engage BSI's consulting practice, implementation work can be scoped, and the two engagements are staffed separately to protect impartiality.
Who Signs the Report
BSI Assurance for ISO certificates. BSI is not a CPA firm and does not issue SOC 2 reports; its SOC 2 work is readiness, and the report comes from a separate licensed auditor you appoint.
Tradeoffs
BSI is the right choice when the ISO certificate's issuer matters to your customers and you either have an ISMS already or will build one with a separate provider. The certifying arm cannot help you close gaps, by design, and the consulting arm is a separate engagement with its own scope and cost. There is no committed readiness date.
6. PwC
Best for: organizations that need a Big Four letterhead and a SOC 2+ report that folds NIST, HITRUST or GDPR criteria into one examination.
Compliance Service Score: 6.6/10
PwC's SOC reporting practice sits inside its audit and assurance business, and it is the closest peer to Deloitte on this page: the same Big Four model, described in more detail on PwC's own service page.
That page names two offerings for SOC 2, a readiness assessment before the examination and the SOC report itself, plus SOC 2+ reports that fold NIST, HITRUST or GDPR criteria into one examination.
Service Overview
Per PwC, the readiness assessment is aligned to the relevant attestation framework and includes gap identification and improvement recommendations before a SOC examination. The examination produces a SOC 1, SOC 2 or SOC 3 report the organization can share with customers and other auditors. PwC recommends starting with the controls that matter most to customers and expanding scope over time.
For ISO 27001, PwC member firms publish gap analysis, ISMS implementation and readiness services, with certification through an accredited PwC entity where independence rules allow.
Pricing and Engagement Model
Quote only, scoped by engagement. PwC publishes no rates for SOC readiness or examination work. Ask what the readiness assessment costs, what it produces, and whether the same team or a separate one performs the examination.
What Stays On Your Team
All of it. A readiness assessment identifies gaps and recommends improvements; the remediation, the policies, the evidence and the program between readiness and examination are the customer's to perform or to source elsewhere.
Who Signs the Report
PwC, as a licensed CPA firm, for SOC reports. For ISO 27001, PwC's own material says certification through its accredited entity depends on the applicable independence requirements. Ask for the independence conclusion in writing for your combination of services.
Tradeoffs
PwC is the right choice when procurement requires a Big Four letterhead, when your financial auditor relationship is already with PwC and consolidation matters, or when you need a SOC 2+ report that combines criteria in one examination.
The model is diagnosis and opinion: the work returns to your team when each engagement ends, and readiness between examinations is not part of the offering described on its site.
7. BDO
Best for: organizations that want a national CPA firm for SOC reporting without Big Four scale, with a free consultation and estimate up front.
Compliance Service Score: 6.6/10
BDO is a national CPA firm with a SOC practice that its own pages describe in three steps: a free compliance consultation, a readiness assessment to identify and rectify gaps, and the audited SOC report. It issues SOC 1, 2, 2+ and 3 reports under the U.S.
SSAE 18 standard and its Canadian equivalent, which makes it one of the companies similar to Deloitte that a mid-market buyer can actually get a conversation with.
Service Overview
Per BDO, the practice evaluates the systems involved in processing data, including cloud platforms, SaaS, infrastructure, software, data streams and financial systems, across security, privacy, confidentiality, availability and processing integrity. The readiness assessment precedes the examination, and BDO offers a report estimate through a free consultation.
Pricing and Engagement Model
Quote only, but BDO's own pages offer a free initial consultation and a SOC 2 report estimate before scoping, which is more than most firms on this page publish. Ask what the readiness assessment costs beyond the consultation and how the Type II observation period is priced.
What Stays On Your Team
Remediation and program operation between readiness and examination. BDO identifies and helps you plan to rectify gaps; your team performs the work.
Who Signs the Report
BDO, as a licensed CPA firm. Ask how the readiness assessment and the examination are staffed and how independence is documented where the same firm performs both.
Tradeoffs
BDO fits an organization that wants a national CPA name without Big Four scale, and a conversation that starts with an estimate rather than a proposal. The model is the same advisory-and-attest structure: the work stays with your team, and there is no committed readiness date.
BDO does not publish an ISO 27001 certification offering on the pages reviewed, so ISO buyers should confirm scope directly.
8. KPMG
Best for: regulated financial services and insurance organizations that want a readiness roadmap and SOC attestation from a firm their board already knows.
Compliance Service Score: 6.3/10
KPMG's IT attestation practice performs SOC 1, SOC 2 and SOC 3 examinations and offers a readiness review beforehand. The published engagement description from one KPMG member firm is unusually specific about what the review involves, which makes it a useful reference for evaluating any firm's readiness offer, Deloitte's included.
Service Overview
Per that published description, the readiness review runs as workshops explaining the control objectives across the Trust Services Criteria, an assessment of current readiness through interviews and documentation review, sample controls and design examples for the client's environment, a mapping of control objectives to ISO 27001, a review of the client's control proposal, and a management report summarizing steps taken and a roadmap.
The attestation engagement then tests design and operating effectiveness and issues the report. KPMG member firms also publish ISO 27001 implementation and certification-preparation services.
Pricing and Engagement Model
Quote only, scoped by engagement. KPMG publishes no rates. Ask what the readiness review costs, what the roadmap deliverable includes, and how the attestation is scoped and priced separately.
What Stays On Your Team
All of it, and KPMG's own description makes the split clear: the firm explains, assesses, provides samples and reviews the client's control proposal. The client proposes the controls, implements them and produces the evidence.
Who Signs the Report
KPMG, as a licensed CPA firm, for SOC reports. ISO 27001 certificates come from a separate accredited body. Ask for the independence conclusion in writing where readiness and attestation come from the same firm.
Tradeoffs
KPMG fits regulated financial services and insurance organizations that want the readiness roadmap and the examination from a firm their board already knows. The roadmap is the deliverable; the road is yours to build. There is no committed readiness date, and the engagement structure is designed for enterprise scale.
9. EY
Best for: organizations that want SOC attestation and ISO 27001 certification coordinated through one Big Four firm with a dedicated global certification body.
Compliance Service Score: 6.2/10
EY issues more than 3,000 SOC reports to more than 900 clients a year by its own figures, and it operates a dedicated, globally accredited ISO certification body, EY CertifyPoint. Its pages describe a SOC readiness assessment ahead of the examination, which makes it the Big Four option for a buyer who wants SOC attestation and ISO certification coordinated through one firm.
Service Overview
Per EY, the readiness assessment typically includes a review of existing controls, a gap analysis, documentation evaluation and actionable recommendations to address gaps before a SOC examination. The SOC reporting and attestation service then examines controls against SOC 1, SOC 2 or ISAE 3402 standards and issues the report. EY CertifyPoint offers ISO management system certification.
Pricing and Engagement Model
Quote only, scoped by engagement. EY publishes no rates. Ask what the readiness assessment costs, what its recommendations document contains, and how ISO certification through CertifyPoint is priced and scheduled separately across the three-year cycle.
What Stays On Your Team
All of it. EY reviews controls, analyzes gaps and recommends; the customer implements, documents and produces the evidence. The program between readiness and examination is the customer's to run.
Who Signs the Report
EY for SOC reports, as a licensed CPA firm; EY CertifyPoint, an accredited body, for ISO certificates. Ask how independence between the readiness practice and the attesting or certifying entity is documented for your engagement.
Tradeoffs
EY fits organizations that want SOC attestation and ISO 27001 certification coordinated through one firm, and those whose customers or boards expect a Big Four name. The readiness deliverable is a gap analysis with recommendations, not a program: the fixing is yours. There is no committed readiness date, and the model is built for enterprise engagements.
How We Built This Guide
We started with the situations that bring people to this search. A readiness assessment quote has landed and needs approval before any work begins. A deal is blocked in procurement on a SOC 2 report or an ISO 27001 certificate. A previous advisory engagement delivered templates and recommendations and the recurring work came back to the internal team.
Someone has asked whether the firm preparing the controls can also sign the report. Finance is reviewing professional services spend and wants a fixed figure and a date rather than a rate card.
Every one of those reduces to the same three questions: after signature, who does the work, who signs the report, and what happens if the date slips? So we organized every firm entry around that axis and applied it to EasyAudit as rigorously as to everyone else.
We then read each firm's own SOC and ISO 27001 service pages and accreditation announcements in September 2026. No firm on this page publishes rates, so no pricing figures appear beyond what the firms themselves publish about their engagement models.
Where a claim about a named firm could not be sourced to that firm's own material, we did not make it; we turned it into a question for you to ask.
The firms named in third-party guides as Deloitte alternatives whose SOC 2 or ISO 27001 readiness offering we could not confirm from their own sites are not on this page.
How To Choose Between Deloitte Alternatives
Six steps, each specific enough to run this week, and each one a question you can put to Deloitte as well.
Step 1: Separate What the Firm Does From What Your Team Does
Ask every firm for a written split of responsibilities: who writes the policies, who maps the controls, who remediates a failing control, who collects evidence, and who talks to the auditor between the readiness report and the examination. Then ask how many hours per week your team should expect in month two.
An advisory firm will describe an assessment and a roadmap. Neither is the work. If the answer to "who fixes it" is your engineer, budget the engineer.
Step 2: Confirm Who Will Sign the Report and Whether Independence Is Documented
SOC 2 reports are issued by licensed CPA firms under AICPA standards; ISO 27001 certificates by accredited certification bodies. Ask which entity will sign yours, whether it is the same organization that prepared you, and if so, how the independence conclusion is documented for that combination of services.
The rules are not a blanket ban, and a firm that offers both should be able to answer in writing. A provider that prepares you and never issues the opinion has removed the question.
Step 3: Ask What the Readiness Assessment Costs and What It Produces
Every firm on this page sells a readiness assessment as a scoped engagement before any remediation begins. Ask for the price, the deliverable, and whether the deliverable is a gap list with owners on your side or a plan the firm will execute. Then ask what happens to the assessment if you choose another firm for the examination.
The readiness assessment that companies like Deloitte charge for is what EasyAudit's Compliance Simulation does free, on your real environment, with the report yours either way; whatever you choose, know the market rate before you approve the spend.
Step 4: Map Every Framework You Will Need in the Next 24 Months
Write down the frameworks a customer, regulator or market entry could require within two years: SOC 2 today, ISO 27001 for the international tenant, ISO 42001 if you ship AI features, NIST CSF 2.0 or CMMC for government-adjacent work.
Then ask each firm whether the second framework is a second engagement, and whether the controls and evidence from the first carry over. Most scope each framework separately while the evidence overlaps 60 to 80 percent. One control library that satisfies up to seven frameworks changes the arithmetic on every framework after the first.
Step 5: Ask What Happens to the Work When the Engagement Ends
Advisory engagements end. Ask each firm who is accountable for your program between the examination and the next one, who detects a control failing in month seven, and who re-does the readiness work when the next framework arrives.
If the answer is your team, then the firm's fee bought a snapshot, and the eleven months between snapshots are yours to cover. A certificate describes one day; the environment changes every week after it.
Step 6: Put the Date and the Consequence in Writing
Ask for a committed readiness date in the contract and ask what happens if it is missed. Firms will decline both, because their fee is not at risk on your outcome; they bill by scope whether you pass or not.
The one provider in this comparison that locks a date at signature and forgoes its fee if the date slips is EasyAudit, and the boundary is stated next to it: the guarantee covers readiness and submission, and the independent auditor or certification body determines the result.
SOC 2 and ISO 27001 Readiness Pricing and Engagement Models in 2026
Two engagement models appear among the firms on this page, and one provider works a third way. No firm publishes rates, so this section describes how each model is priced rather than what it costs; the market figures that follow come from third-party guides and are attributed as such.
Advisory and attestation, billed by scope. Deloitte, PwC, EY, KPMG, BDO, Schellman, A-LIGN and Coalfire scope readiness and attestation as separate engagements and quote each.
Third-party guides put an external SOC 2 readiness assessment at $10,000 to $40,000 depending on size, consultant time at $150 to $300 an hour for remediation help, and the Type II examination itself at $15,000 to $50,000 or more, with Vanta's own SOC 2 cost guide noting that large enterprises working with a Big Four firm can pay low six figures for the audit alone.
For ISO 27001 the certification body's Stage 1, Stage 2, surveillance and recertification audits are priced across a three-year cycle. In every case the remediation between readiness and examination is billed separately or done by your team.
Certification body plus separate consulting. BSI Assurance prices certification audits by scope; BSI's consulting practice prices implementation help as a separate engagement, kept apart to protect impartiality. Two contracts, two scopes, two invoices.
Outcome-priced service. EasyAudit runs the free Compliance Simulation on your own environment first, then fixes the investment and the readiness date at signature, with its fee at risk if the date is missed. There is no readiness assessment charge and no rate card. Auditor and certification body fees remain separate, because the independent auditor issues the result.
The questions buyers ask about the engagement, answered
"We already have a Big Four relationship." Consolidation is a real benefit, and if your financial auditor is Deloitte or a peer, ask them first what the SOC readiness engagement includes and who performs the remediation. Then ask for a decision-grade comparison on the date and the total cost, including your team's hours.
"How long will it take and how much will it cost?" With an advisory firm, the readiness assessment answers the first half after you pay for it. EasyAudit's Simulation answers both on your own data before you sign anything, in about 75 minutes of scheduled time across two calls.
"We need SOC 2 and ISO 27001. Is that two engagements?" With most firms, yes, or one engagement with two scopes and two teams. With one control library, one evidence set is mapped to every framework, and the program carries 60 to 70 percent fewer controls.
"We tried a consultant before and the work came back." That is the model, not a failure of the consultant. The Simulation is a near-zero-risk diagnostic on your real environment, free, and if you proceed the work transfers to us and stays transferred.
Engagement Model Comparison
Provider | Pricing | Model | Named expert leads | Policies written for you | Continuous monitoring | Signs the report or certificate | Committed readiness date |
EasyAudit | Fixed at signature from the free Simulation | Outcome-priced service | ✓ | ✓ | ✓ | Never. An independent auditor or certification body issues the result. | ✓ |
A-LIGN | Quote only (A-SCEND free tier) | Advisory and attestation | – | – | Add-on | ✓ | – |
Coalfire | Quote only | Advisory and attestation | – | – | Add-on | ✓ | – |
Schellman | Quote only | Advisory (separate entity) and attestation | – | – | – | ✓ | – |
BSI | Quote only | Certification; separate consulting | Add-on | Add-on | – | ISO only | – |
PwC | Quote only | Advisory and attestation | – | – | – | ✓ | – |
BDO | Quote only; free consultation and estimate | Advisory and attestation | – | – | – | ✓ | – |
KPMG | Quote only | Advisory and attestation | – | – | – | ✓ | – |
EY | Quote only | Advisory and attestation; ISO via CertifyPoint | – | – | – | ✓ | – |
As of September 2026. No firm in this comparison publishes rates; market ranges in the text above are attributed to third-party guides. "Add-on" means the capability is available through a separate practice, entity or partner. "Named expert leads" means a named person owns the engagement outcome, not a rotating engagement team. EasyAudit is not an audit firm or a certification body: it never signs, issues or attests to any report or certificate, and no cell in this table should be read otherwise. An independent CPA auditor or accredited certification body issues the result in every EasyAudit engagement.
Key Capabilities to Look for in a SOC 2 and ISO 27001 Readiness Provider
1. A Committed Readiness Date With a Defined Consequence
If the firm's fee is safe whether or not you are ready on time, the timeline is a hope. Look for a readiness date locked at signature and a stated consequence if it is missed. Then look for the boundary next to it, because any provider that promises the audit result itself is promising something only the independent auditor controls.
2. Multi-Framework Control Mapping
If your second framework is quoted as a second engagement, the provider is not mapping controls; it is copying them. Look for one control library that every framework maps into, so a control implemented once satisfies every framework that asks for it and one evidence set covers all mappings.
Ask what percentage fewer controls you will carry running SOC 2 and ISO 27001 together versus separately. In EasyAudit's program the answer is 60 to 70 percent.
3. Continuous Compliance Between Examinations
If your report describes last March and your environment changed every week since, you have been exposed for eleven months. Look for monitoring that checks controls daily against your connected systems, detects drift the day it appears, diagnoses the cause and prescribes the fix. Advisory engagements end; ask who is watching in month seven.
4. Named Human Accountability
If nobody at the provider is accountable for your outcome after the engagement closes, your outcome is your problem. Look for a named expert who owns the program, checks every piece of work, coordinates the auditor and answers to a date. An engagement team answers questions until the scope ends. An accountable person owns results.
5. Evidence an Auditor Will Accept
If the auditor rejects your evidence in the observation window, the date moves. Look for approvals recorded with who and when, a trail enforced at the database level so the application cannot bypass it, and evidence traceable to its source system rather than to a screenshot. Ask whether independent CPA auditors were involved in designing the evidence standards. The question every architectural choice should answer: would an auditor trust this?
6. A Clear Answer to Who Signs
If the firm that built your controls also plans to sign the opinion on them, you need the independence conclusion in writing before you scope. Look for a provider that either separates the two in its structure, as Schellman does, or never signs at all, as EasyAudit does, so the auditor gets a read-only view and looks through but cannot touch.
Which Option Is Right for Your Organization?
If procurement requires a Big Four letterhead, or your financial auditor is already one of them and consolidation matters, ask Deloitte, PwC, EY or KPMG the six questions above and compare the answers.
PwC publishes the clearest SOC 2+ combined reporting and, per its member-firm material, certifies ISO 27001 through an accredited PwC entity in some regions where independence allows; EY operates a dedicated global certification body, EY CertifyPoint.
If you want the readiness assessment and the signed report from one specialist firm at specialist scale, choose A-LIGN, Schellman or Coalfire, and confirm which entity signs and how independence is documented. If the ISO certificate's issuer is what your customers care about, BSI. If you want a national CPA firm that will give you an estimate before a proposal, BDO.
If a deal or a date is waiting on the report, nobody internal wants to own the work, and the quote in front of you is for an assessment that hands the remediation back, choose the provider that performs the work and puts its fee behind the date. That is EasyAudit. Run Your Simulation and decide from your own numbers.
Is EasyAudit Worth It?
Against a single readiness assessment, only if you intend to act on it. If you want a gap list and a roadmap and your team will do the rest, an advisory engagement is the rational purchase.
Against what a consulting-led program costs a regulated company, the comparison changes. Add the paid readiness assessment before any work begins. Add the advisory hours during remediation and the internal hours from engineers hired to build product. Add the second framework scoped as a second engagement.
Add the eleven months a year between examinations when nobody at the firm is accountable, and the deal that waits while your team scrambles. Consultants and human-centric tools cost ten to a hundred times more manual hours than Autonomous Compliance, and none of them puts a fee at risk on your date.
EasyAudit is the right purchase when the outcome is what you are buying and the work is what you want to stop doing. The Simulation exists so you can check that on your own environment before spending a dollar, which is also what a readiness assessment is supposed to do. Compliance runs on someone's time. We changed whose.
FAQs
Can the same firm prepare us for SOC 2 and also issue the report?
Sometimes, within limits. Under AICPA independence rules a firm that designs and implements controls generally cannot attest to those same controls where doing so impairs its independence, so the readiness scope must be bounded and the conclusion documented. Ask any firm offering both for that documentation in writing.
How much should a SOC 2 or ISO 27001 readiness assessment cost?
Third-party guides put an external readiness assessment at $10,000 to $40,000 depending on size, before any remediation. No firm on this page publishes a rate. EasyAudit's Compliance Simulation does the same diagnostic work free, on your real environment, in about 75 minutes, and the report is yours either way.
How long does SOC 2 and ISO 27001 readiness take?
It depends on your gaps, your systems and who performs the remediation, so question any fixed number of weeks. A SOC 2 Type II observation window then runs three to twelve months, and ISO 27001 adds Stage 1, Stage 2 and annual surveillance. EasyAudit's Simulation produces a dated timeline before you sign, then locks it.
Can any provider guarantee that we pass the audit?
No. The independent CPA auditor or accredited certification body alone determines the result, and any provider implying otherwise should be questioned. What a provider can commit to is readiness: EasyAudit guarantees you will be audit-ready and submitted by the committed date, or you do not pay, for eligible engagements.
What happens to compliance work after a consulting engagement ends?
It returns to your team. Advisory engagements deliver a gap list, recommendations and a roadmap; the recurring work of policies, evidence, remediation and auditor liaison is yours between examinations. Ask each firm who is accountable in month seven. EasyAudit keeps the work after the first audit, with continuous monitoring.
Do these options work in Microsoft-heavy or on-premise environments?
The large firms have deep experience in physical and regulated operations, which is a real strength; platforms often do not. Ask each provider to show evidence collection from Entra ID, Intune, Purview and any on-prem system. EasyAudit is built for those operations; the named expert attends the facility when controls require it.